LECS Platform: Plug & Play NDR for internal network visibility.
Hardware or virtual appliance that analyzes internal traffic across IT, OT, IoT and medical networks, correlates anomalies with proprietary engines and responds when you decide. Up and running in 10 minutes, supporting NIS2 compliance.
Proprietary technology protecting the internal network: it sees the east-west traffic that firewalls and EDR miss.
Deep detectionEvery connection analyzed down to the payload, across over 100 IT and OT protocols.
Invisible to attackersStealth mode: no exposed services, no ping response.
Real-time responseRAISES contains the threat on traffic as soon as it is detected, without stopping operations.
Parallel enginesAI correlation, severity scoring, OT analysis and asset intelligence.
The LECS Platform range.
Same technology, same dashboard: choose the analysis capacity based on traffic and number of sites. Every line includes a hardware or virtual appliance, central dashboard, detection & response engines, email and Telegram notifications, automatic reports and warranty.
LECS PLATFORM SMALL
Agile protection for small facilities and branch offices: detection & response with a Cloud dashboard, on compact hardware or as a virtual version.
LECS PLATFORM MEDIUM/LARGE
For manufacturing companies and multi-site organizations: more analysis capacity for dense networks and centralized monitoring of every site.
lecs platform CORPORATE
Maximum protection for large networks, critical infrastructures and public bodies: the highest traffic volumes, On-Premises installation with data and logs inside the company perimeter.
Appliance, virtual, embedded or with dedicated modules: LECS adapts to the infrastructure you already have.
Appliance
The LECS hardware appliance: it connects to the switch mirror port and is operational in about 10 minutes, in the Small, Medium/Large and Corporate lines.
The confidence of those who have chosen certainty.
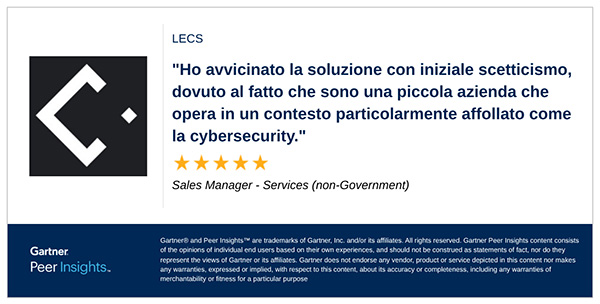
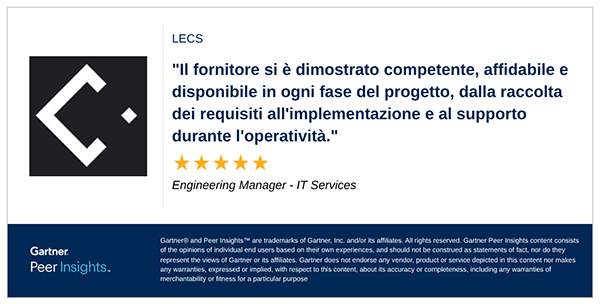
≈245,000 protected hosts in 24 countries, 230 partners and a 98% renewal rate. Here is what customers say on Gartner Peer Insights.
Frequently asked questions about LECS Platform
How do you ensure business continuity during installation?
Zero downtime: LECS works in parallel with the network, on a copy of the traffic, with no interruptions and no changes to existing devices. A typical installation takes about 10 minutes.
Is the platform compatible with industrial systems (OT) and legacy machinery?
Yes. LECS is agentless: it passively monitors PLCs, SCADA and medical devices that cannot host security software, including End of Life systems. For new machines, manufacturers can integrate LECS Embedded.
Where do data and security logs reside?
It depends on the deployment. In the Cloud version the dashboard resides on servers in Italy. In the On-Premises version, logs and dashboard stay on the Aggregator, inside the company infrastructure, supporting the strictest requirements, including NIS2 and ACN.
Does LECS replace the antivirus or firewall already in place?
No, LECS is complementary. While firewalls protect the perimeter and antivirus software protects endpoints, LECS closes the “blind spot” of internal visibility (Network Detection & Response). It identifies lateral movement and threats that have already bypassed external defenses.
How are alerts and notifications handled?
Automatically: events are correlated and classified by severity, and you receive email and Telegram notifications plus periodic reports. Auto Suppression and fine tuning cut false positives, so you focus only on real risks.