
The cyberattacks that have hit supermarkets and food supply chain operators across Europe in recent weeks show very clearly that cybersecurity is no longer just about data, computers and digital services.
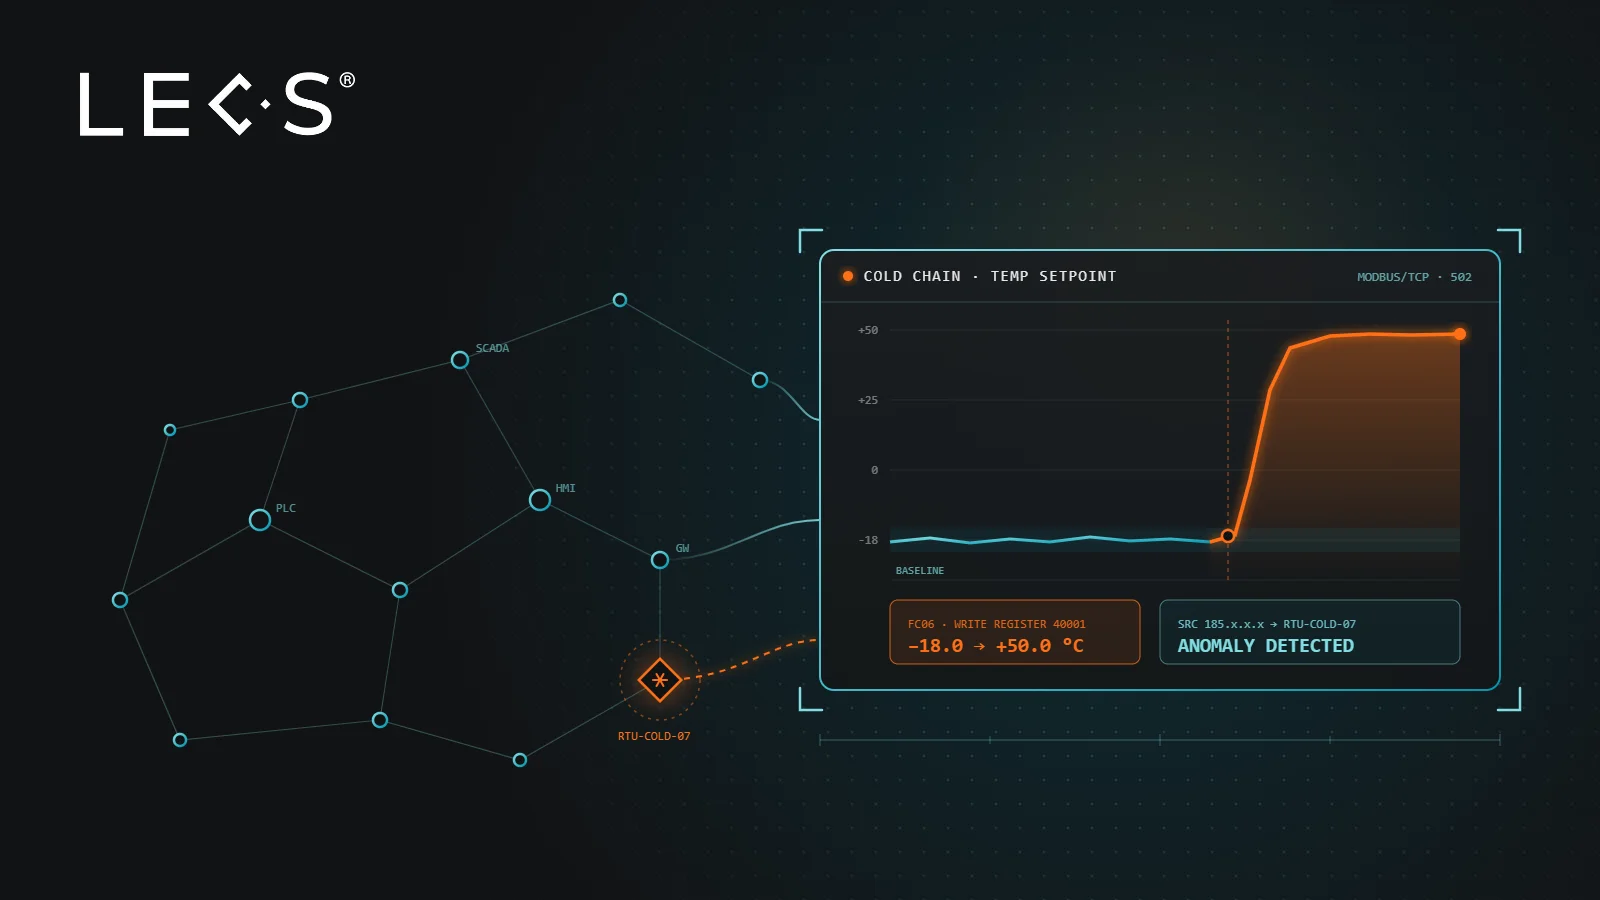
When a connected system controls a physical process, a cyber incident can have equally physical consequences: changing the temperature of a plant, stopping a service, spoiling products and raw materials, or bringing operations to a halt.
This is what is happening across the European cold chain, where several incidents have affected the control and remote maintenance systems of refrigeration plants.
These cases are part of a much broader picture: in the first half of 2026, according to Clusit data reported by ANSA, 4,911 serious cyber incidents were recorded worldwide, more than double the previous half-year and the highest figure the association has ever recorded in a single six-month period.
From France to a Europe-wide wave
The most significant precedent dates back to 12 October 2026, when systems used to manage refrigeration plants were compromised in France.
A few weeks later, the phenomenon spread.
On 2 November, incidents or anomalies affecting supermarket refrigeration systems were reported in several European countries, including Belgium, Sweden, Estonia, Luxembourg, Ireland and the Netherlands. In some cases, according to ANSA, freezer temperatures were reportedly raised remotely to as much as +50 °C, forcing stores to dispose of food and leading some outlets to close temporarily.
The European Commission described the recurrence of these incidents as “deeply concerning”, stressing that cyberattacks can disrupt services, hit businesses and have a direct impact on everyday life.
The issue therefore goes beyond the individual supermarket: it concerns the resilience of an entire supply chain made up of stores, warehouses, logistics operators, plants, maintenance providers and distributed remote control systems.
The attacks have also reached Italy
Cases also emerged in Italy on the same day.
In Sicily, the temperature parameters of refrigeration systems were altered at several Coop stores, causing food to spoil. The company later confirmed that the attack had targeted the remote control system of its frozen food cabinets.
Italy’s National Cybersecurity Agency (ACN) also reported receiving a notification from a Tuscan contract catering company and detecting a further attack on a frozen food producer in Emilia. ACN has since stepped up monitoring of the sector.
Investigations into the origin of the incidents and any links between them are still ongoing. What is already clear, however, is the target: digital systems used to govern essential physical processes.
Not an isolated problem: cyber pressure on organisations is growing
The incidents in the retail sector come at a time of generally intensifying cyber activity.
The ENISA Threat Landscape 2026 identifies ransomware as the incident type with the greatest short-term impact in the European Union and highlights how the growing interdependence between digital systems is steadily widening the attack surface. Public administration, transport, manufacturing, services and finance are among the most affected sectors.
In Italy, the Clusit report also shows a shift in the nature of incidents: the relative weight of hacktivism is declining while cybercrime against businesses is rising, with manufacturing ranking first among the sectors hit in the first half of 2026.
Techniques are evolving too. In October, attacks were reported in Japan against companies in retail, logistics and finance in which an artificial intelligence system was allegedly used to support offensive activities.
The common denominator is therefore the ability to know and observe what is really happening inside infrastructures, especially as IT, OT, IoT and third-party systems become increasingly interconnected: the hardware and software used to monitor or control physical processes, such as controllers, sensors, actuators, supervisory systems and devices that regulate temperatures, compressors and defrost cycles.
In retail, these systems coexist with traditional IT infrastructure, store networks, management systems, IoT devices and connections used by maintenance providers and suppliers.
The same applies to many other environments: HVAC and building automation, logistics, energy infrastructure, production plants, control systems and connected medical devices.
Every new device and every remote access point can become yet another element of the attack surface to be known and protected. Which systems control the plants, who can reach them, and how can unauthorised changes be detected?
The checks recommended by ACN
Following the incidents, ACN urged retail operators, food logistics companies, industrial refrigeration firms and maintenance providers to apply the security measures already recommended after the French incidents.
Priorities include:
- checking whether control and remote maintenance systems are exposed to the Internet;
- segregating these systems in protected environments, separate from corporate IT networks;
- strengthening remote access with VPN and multi-factor authentication;
- reviewing accounts and privileges;
- updating or replacing devices that are no longer supported;
- checking the integrity of operating parameters and acting quickly when anomalies occur.
Protection, however, does not end with removing an exposed access point.
You also need to know which assets exist, how they communicate with each other and what is actually happening on the network.
This is exactly where visibility becomes central.
From access control to Unified Visibility
Firewalls, authentication, segmentation and device updates remain fundamental measures.
But in distributed and hybrid infrastructures, you also need to be able to recognise what happens after a connection has been established.
A connection can be technically permitted and, at the same time, carry an anomalous command for the process it controls.
This is why protecting IT and OT environments requires a view that correlates assets, communications, protocols, anomalies and operational context.
This is the principle behind the LECS ecosystem, designed to provide a single point of control over IT, OT, IoT and IoMT environments while integrating with the existing security stack.
What LECS can do: from the cold chain to any OT environment
Retail is only the most recent example. The same problem affects manufacturing, logistics, energy, healthcare, building automation and any organisation where IT and OT coexist. And the first step is often a simple one: knowing exactly what is connected to the network.
1. ORION: knowing which assets exist
With ORION Asset Intelligence, LECS makes it possible to build and maintain a view of the assets in the infrastructure through Asset Discovery and Asset Inventory.
The analysis can cover IT, OT, IoT and IoMT devices and collects useful information such as:
- detected devices and inventory changes;
- firmware versions;
- active services and protocols;
- known vulnerabilities and CVEs;
- legacy or End of Life devices;
- relationships and communications between assets.
This means you can also identify devices that had never been inventoried and have an up-to-date baseline for setting remediation priorities.
ORION can also represent relationships using a Zones & Conduits model, helping you understand infrastructure segmentation and communications between different areas.
In a supermarket, for example, it becomes possible to understand which systems belong to the refrigeration infrastructure and which other network components they communicate with.
2. ANTLIA: observing what happens in the OT process
Knowing a device, however, does not yet mean knowing what it is doing.
ANTLIA extends analysis to OT, IoT and IoMT environments and monitors supported industrial protocols to identify activities and behaviours that deviate from expected operation.
In a cold chain scenario, this means observing not only that a controller is communicating, but also detecting critical or unauthorised commands and anomalous changes to process parameters, when this information is available in the analysed traffic.
Cybersecurity must also be able to understand what is being commanded to the plants, linking network behaviour to the operation of the physical process.
ANTLIA is agentless, which is particularly important in OT environments, where installing software directly on controllers or modifying legacy systems may not be possible or advisable.
Centralised dashboards, reports and notifications bring information together into a single management view, while API and Syslog enable integration with existing technologies such as SIEM and other tools in the security stack.
The goal is not to replace firewalls, EDR, SIEM or segmentation measures, but to add the Unified Visibility needed to understand assets, communications and anomalies across different environments.
Know first, then protect
The attacks on the cold chain make a problem that now affects many sectors particularly tangible.
A cyberattack does not need to wipe a database to cause serious damage. Changing a parameter, tampering with a remote control system or compromising a seemingly minor device can be enough.
That is why the question is no longer just “Is my network protected?”, but also:
“Do I know which devices run my processes, how they communicate, and would I notice if someone started changing their behaviour?”
This visibility is the starting point for a truly effective cybersecurity strategy across IT, OT, IoT and IoMT environments.