
When we talk about hackers, we immediately picture someone sitting behind a screen, busy breaking into systems and stealing data. This is a one-sided portrayal of a much more multifaceted figure.
IN SUMMARY – A hacker studies systems, networks, and devices to understand them, modify their behavior, and achieve a goal. This article traces the history of hackers and the evolution of the hacker mindset, from the earliest communities to the classifications of white, gray, and black hats, and the taxonomy of threat actors. MITRE ATT&CK rounds out the picture by describing tactics and techniques observed in real-world attacks.
Who is a hacker? A hacker is someone who thoroughly studies computer systems, networks, or devices to understand how they work, modify their behavior, and achieve specific goals.
In addition to their tactics, what sets them apart from one another are the contexts, permissions, and purposes for which they use their skills. Understanding who hackers are and how they differ from other threat actors can help companies assess risk more accurately and set priorities for corporate cybersecurity.
The History of Hackers: The Birth and Evolution of the Hacker Mindset
Here, we trace some key episodes in the evolution of hackers to identify the turning points that have shaped their mindset and methods over time.
The MIT Hackers: From Toy Trains to the First Computers
The hacker mindset originated long before the Internet. It took shape at the Massachusetts Institute of Technology in the 1950s and 1960s.
The Tech Model Railroad Club brings together engineers who are passionate about model trains. Their curiosity and love of experimentation give them the opportunity to study the systems on which electric trains run and to come up with unexpected solutions to overcome their limitations—creative solutions known, in fact, as “hacks.”

This same mindset unites model train enthusiasts with the first professionals who had access to computers and were exploring research-grade machines intended for very different uses.
On MIT’s PDP-1, one of the first interactive transistor-based computers, *Spacewar!*—one of the earliest video games—was created, while Peter Samson developed pioneering software for digital music synthesis.
TAKEAWAY – These are examples of a central question in hacker thinking: What else can this machine do? Can it turn computation into music? Can it turn a screen designed to display data into a playground?

The Homebrew Computer Club and Phreakers: Two Paths in Hacker Culture
In the 1970s, the hacker mindset spread beyond universities and took root in informal communities, following different paths. One such community wasthe Homebrew Computer Club.
By assembling early PCs such as the Altair 8800, participants put their skills to the test to earn the recognition of their peers through the technical merit of their proposals. Here, software and technical solutions are developed that transform rudimentary machines into increasingly usable and versatile tools. It is the cradle of the nascent mass-market computer industry.

At the same time, phreakers apply the same spirit of exploration to telephone networks, but in a transgressive and clandestine manner. Using electronic devices, they replicate the frequencies used by the network to route calls, enabling them to make free calls or manipulate the network’s operation.
Phreaking marked the beginning of clashes between hackers, corporations, and the law. The cases of John Draper, known as Cap’n Crunch, and Kevin Mitnick—both of whom were phreakers at the start of their careers—became famous.
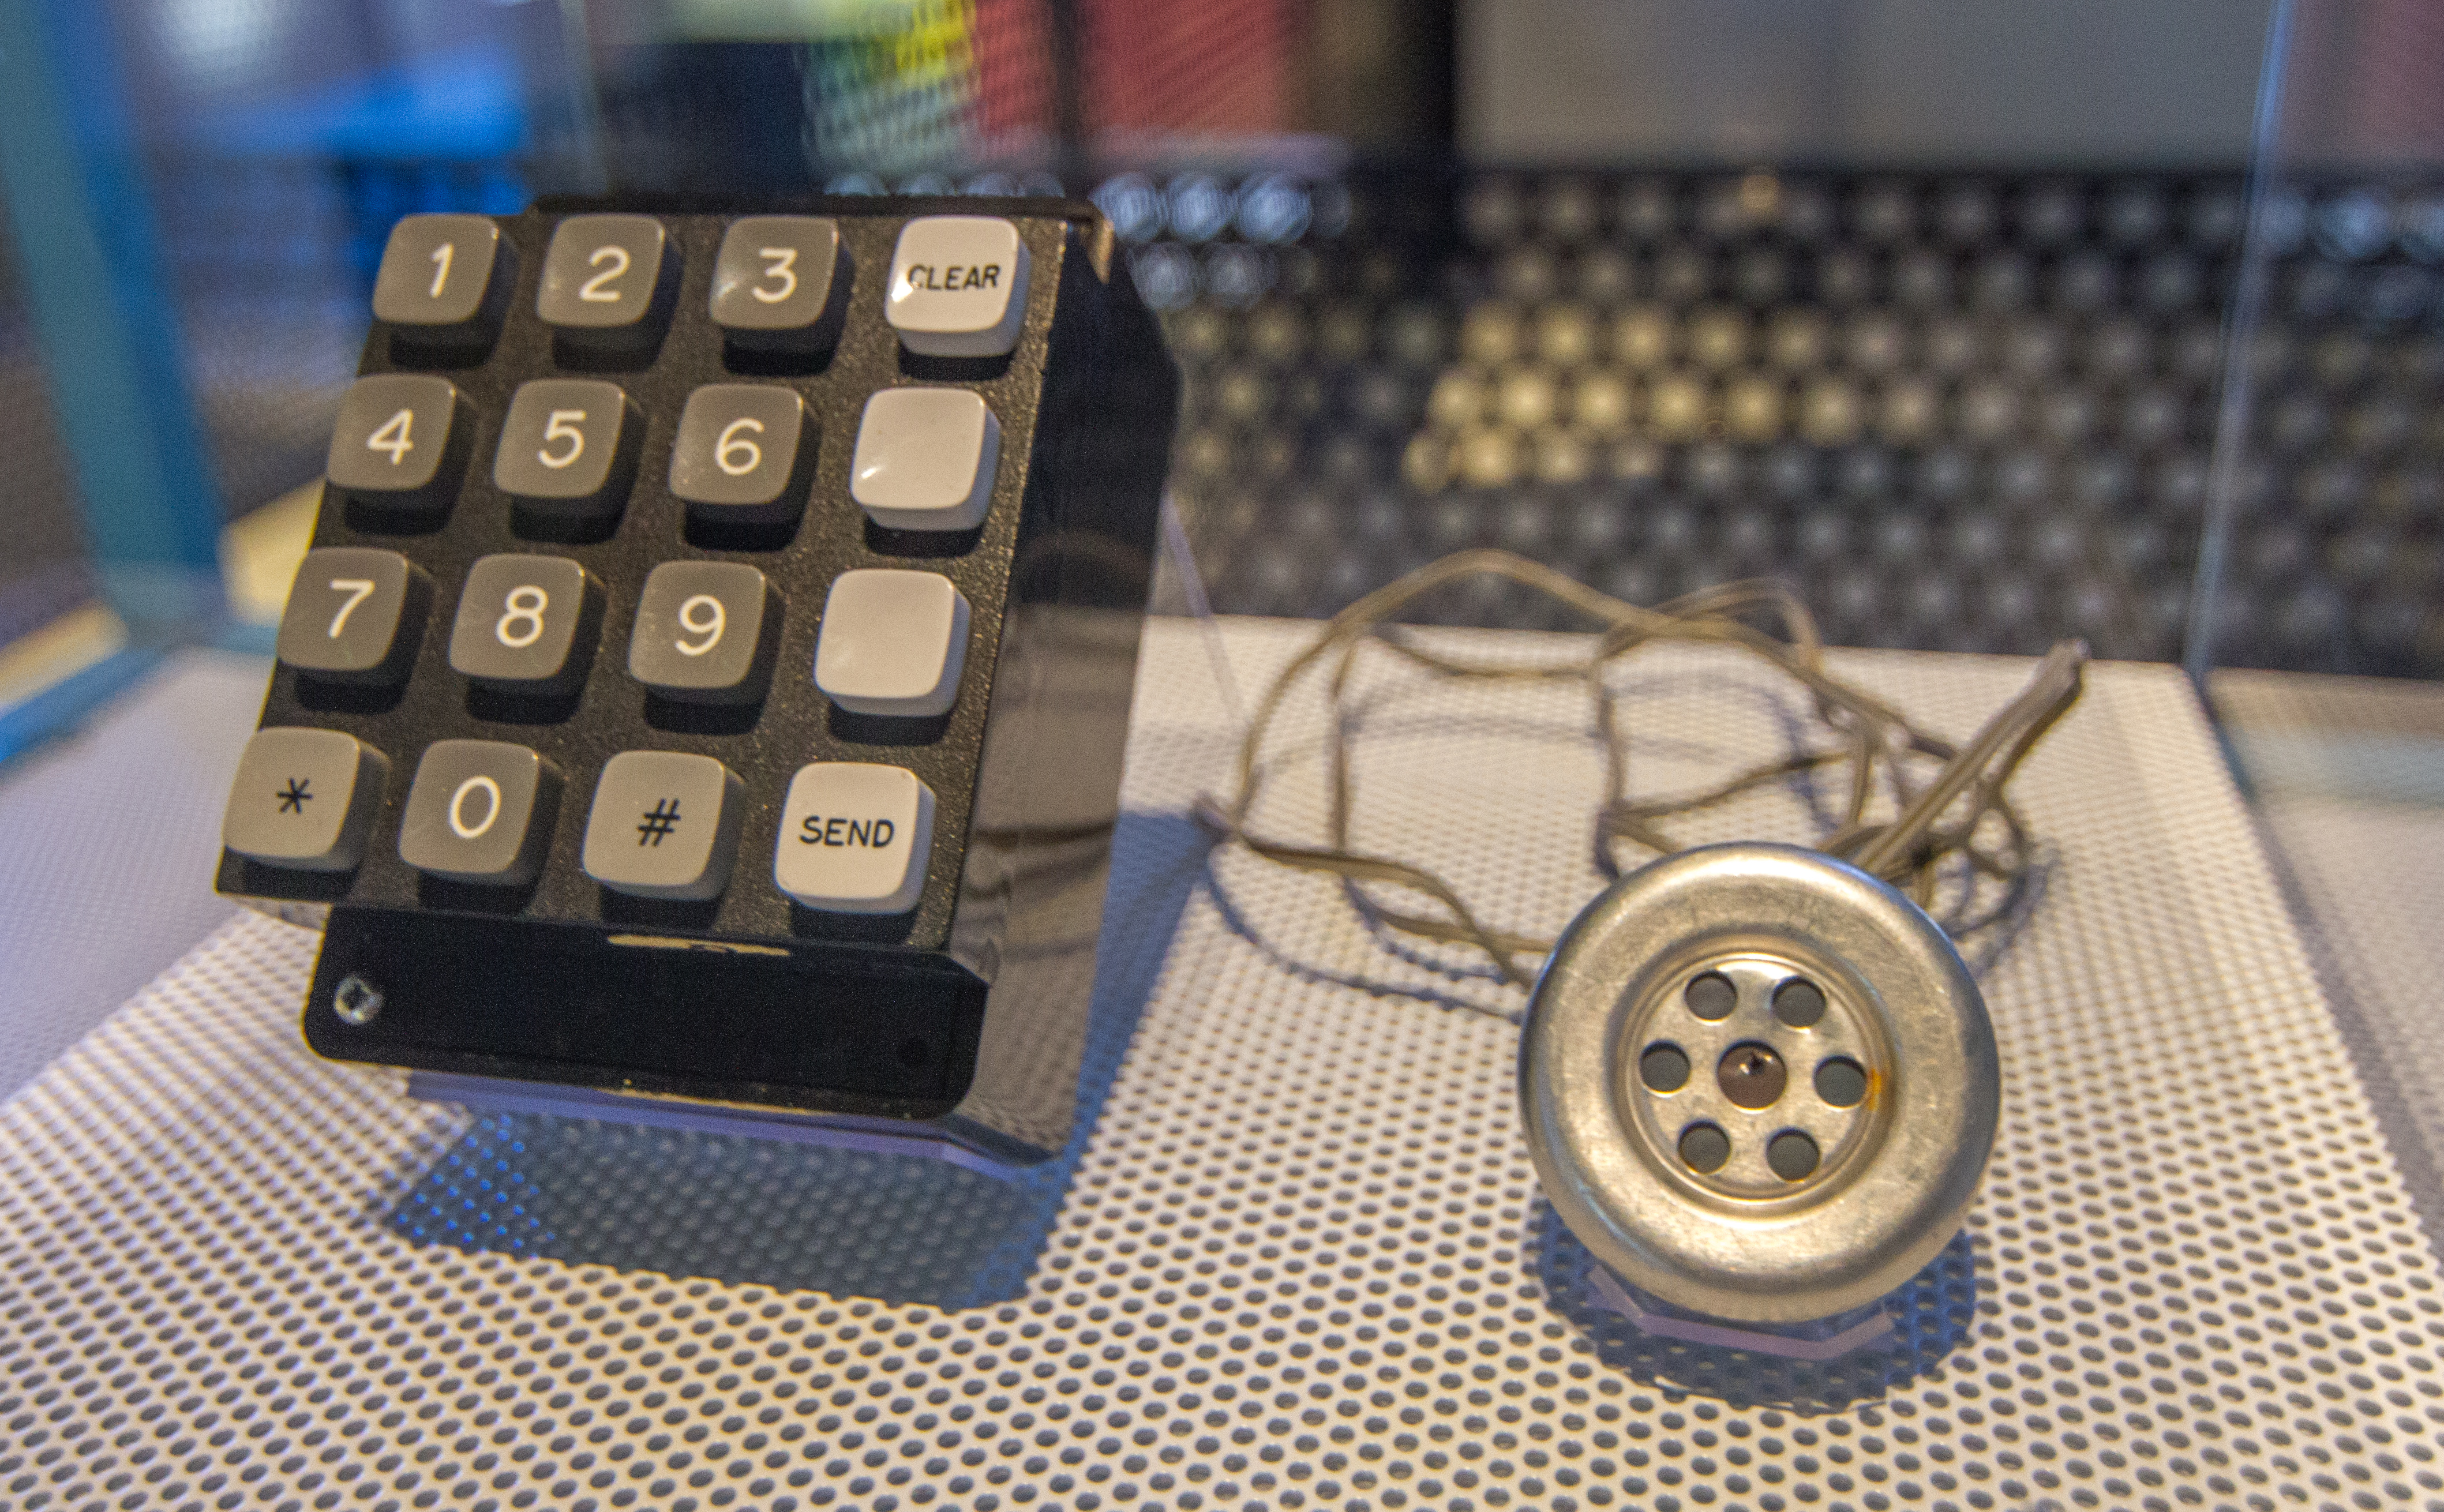
TAKEAWAY – The same motivation can lead to innovation and collaboration, or to illegal practices. To assess the risk, it is therefore not enough to look for an economic advantage or an explicit intent to cause harm: curiosity, technical challenges, and reputation within the community can make even a system with no direct economic value attractive and lead to tangible consequences.
Hackers and Cybercrime: *WarGames* and the Case of the 414’s.
A hacker, therefore, cannot be defined by a single motivation: to understand a hacker, one must distinguish between intentions, skills, and the impact caused. Curiosity, even in the absence of destructive intentions, does not rule out the risk.
In 1983, the movie *WarGames* glorified the image of the child prodigy and sparked an interest in hacking among many young people. Around the same time, the FBI identified and arrested the 414s, a group of teenagers with limited technical skills (who would one day be called “script kiddies”) who had nevertheless managed to gain access with remarkable ease to dozens of strategically important computer systems.
Hackers as a Public Threat: The Morris Worm.
Even constructive intentions are risky when the methods and the scale of their consequences are unclear.
In an effort to uncover and demonstrate vulnerabilities, a talented student at Cornell University, Robert T. Morris, carried out the first denial-of-service attack in the history of the Internet in 1988.
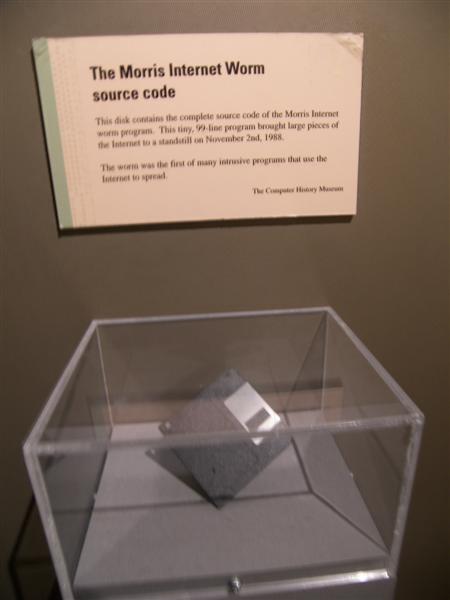
Photo: Go Card USA, CC BY-SA 2.0, via Wikimedia Commons.
Morris claims his actions were motivated by security concerns, but he acts without authorization or controlled procedures. His worm caused damage estimated at between $200 and $53,000 per affected computer (approximately 6,000) and caused downtime in the systems of universities, government agencies, and military facilities.
TAKEAWAY – Inexperienced but curious or bored individuals can compromise sensitive systems when they encounter weak access controls and insufficient oversight. Highly competent individuals with good intentions can cause serious damage if they do not follow established procedures and act without authorization. The risk depends on many variables.

White hat, black hat, and gray hat: the main types of hackers.
The 414s and Morris Worm cases show that skill and intent alone are not enough to define a hacker or the risk he or she poses. Over time, it has become necessary to develop classifications that take various aspects into account.
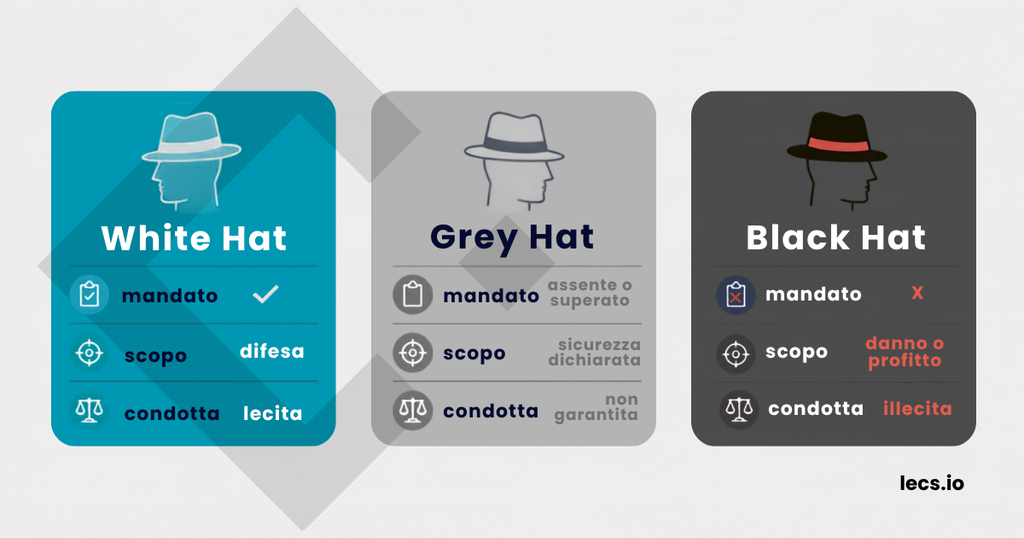
A useful distinction for categorizing different types is that between white hat, gray hat, and black hat.
Three “categories” that describe three ways of applying one’s skills in relation to authorization, intent, and legality.
| Profile | Authorization | Methods and Purposes |
|---|---|---|
| White hat – ethical hacker | Formally authorized, with a predefined purpose | It identifies vulnerabilities and helps improve the organization’s security. |
| Grey hat – unauthorized action | They did not submit a quote, or they are operating beyond the scope of the authorization they received. | It can identify or demonstrate a vulnerability by stating a security-oriented purpose. |
| Black hat – criminal use of skills | Operates without authorization and for unlawful or harmful purposes. | It exploits vulnerabilities, credentials, or intrusion techniques to steal data, commit fraud, distribute malware, extort money, or sell access. |
What Is a Threat Actor: From Hacker to Threat Actor.
In cybersecurity jargon, the term “ threat actor” refers to an individual or group capable of posing a risk and causing harm. The concept encompasses actors with widely varying levels of expertise, motivation, organization, and resources.
For cybersecurity companies and professionals, understanding threat actors can help them distinguish one scenario from another and set defense priorities.
| PROFILE | MOTIVATION AND TRAITS | WHY IT’S USEFUL TO KNOW THIS | SEE ALSO |
|---|---|---|---|
| CYBERCRIMINALS | Profit | It helps identify data, credentials, and systems that are easier to monetize. | An in-depth article is coming soon to the LECS blog |
| INSIDER THREAT | Legitimate Access and Internal Risk | It helps identify data, credentials, and systems that are more vulnerable from within | An in-depth article is coming soon to the LECS blog |
| SCRIPT KIDDIES & THRILL SEEKERS | Challenge, recognition, and satisfaction. | This helps ensure that opportunistic and easily replicable threats are not underestimated: even limited skills can have an impact when they encounter exposed services or weak credentials. | |
| HACKTIVIST | Ideology | It helps assess the risks of service disruption, data exposure, and reputational damage, taking into account how the geopolitical and media landscape may influence targets and timing | An in-depth article is coming soon to the LECS blog |
| EXTREMIST ACTORS & CYBERTERRORISM | Ideology with Coercive Aims | It allows you to build scenarios that are proportionate to intent and impact. | An in-depth article is coming soon to the LECS blog |
| SPONOSRED & APT GROUPS | Geopolitics | It helps protect strategic information and interpret activities that are subtle and long-term. | An in-depth article is coming soon to the LECS blog |
Classifications help provide context, but they oversimplify a complex and ever-changing reality. Black-hat and gray-hat classifications can overlap with those of threat actors, making it extremely difficult for companies and professionals to interpret the cybersecurity risk landscape.
- A cybercriminal can purchase access obtained by another group;
- An insider can facilitate an external campaign, even unintentionally;
- A hacktivist group can use tools developed by criminals, such as renting a botnet, keeping thousands of compromised devices on standby to be activated to carry out DDoS attacks;
- A state-sponsored group can conceal its activities behind a different identity.
The MITRE ATT&CK framework compiles behaviors observed in the real world and provides a common language for linking technical indicators to potential attacker objectives.
Understanding attackers helps in developing risk scenarios. But an attack is not limited to a single technical move: it is often the result of a series of linked actions, from the initial penetration to the achievement of the objective.
In this feature, we analyze the concept of the Kill Chain and explain why perimeter defenses, while necessary, are not sufficient to minimize cybersecurity risk in a company.
Why Understanding Hackers Helps Improve Corporate Cybersecurity
- We analyzed the key milestones in the history of hackers, showing how the main elements of a shared mindset have evolved.
- We have introduced the “colored hats” classification system, which categorizes hackers based on their methods and authorization levels, as well as the threat actor taxonomy, which helps clarify their motivations, resources, and role in the threat;
- Finally, we refer readers to MITRE ATT&CK for further details on the tactics and techniques observed in real-world attacks and, where documented, those associated with specific groups.
For a company, understanding the attacker means assessing the risk from the attacker’s perspective. Defending a system also requires the ability to see it through the eyes of someone looking for an unexpected way to use it.
It is with this mindset that network visibility becomes part of the strategy: it allows us to recognize how a connection translates into activity, movement, and potential impact.
Defending a system also requires the ability to see it through the eyes of someone looking for an unexpected way to use it.
From a hacker mindset to network visibility.
From this perspective, defense is not a static stance, but a dynamic interpretation of the infrastructure.
This visibility is particularly useful after initial access, when an attacker attempts to gain access to critical data and services through activities that—even if they appear legitimate—leave traces in network traffic.
LECS® applies this approach through continuous analysis of network traffic and behavior, helping to build visibility, context, and responsiveness while keeping operational continuity at the forefront.
Close the cybersecurity loop.
LECS® supports continuous, automated and auditable security,
helping to turn regulatory requirements into operational capabilities.